


The same supplier, verified again and again
Registration, security screening and certifications are re-checked program by program, and each check
Documents travel separately from the goods
Certificates and test reports arrive by email, get re-keyed, and are hard to trace back to the item they describe.
Availability is invisible until a tender closes
Program offices rarely see what qualified suppliers already hold in stock, especially smaller firms deep inthe supply base.

Registration, security screening and certifications are re-checked program by program, and each check

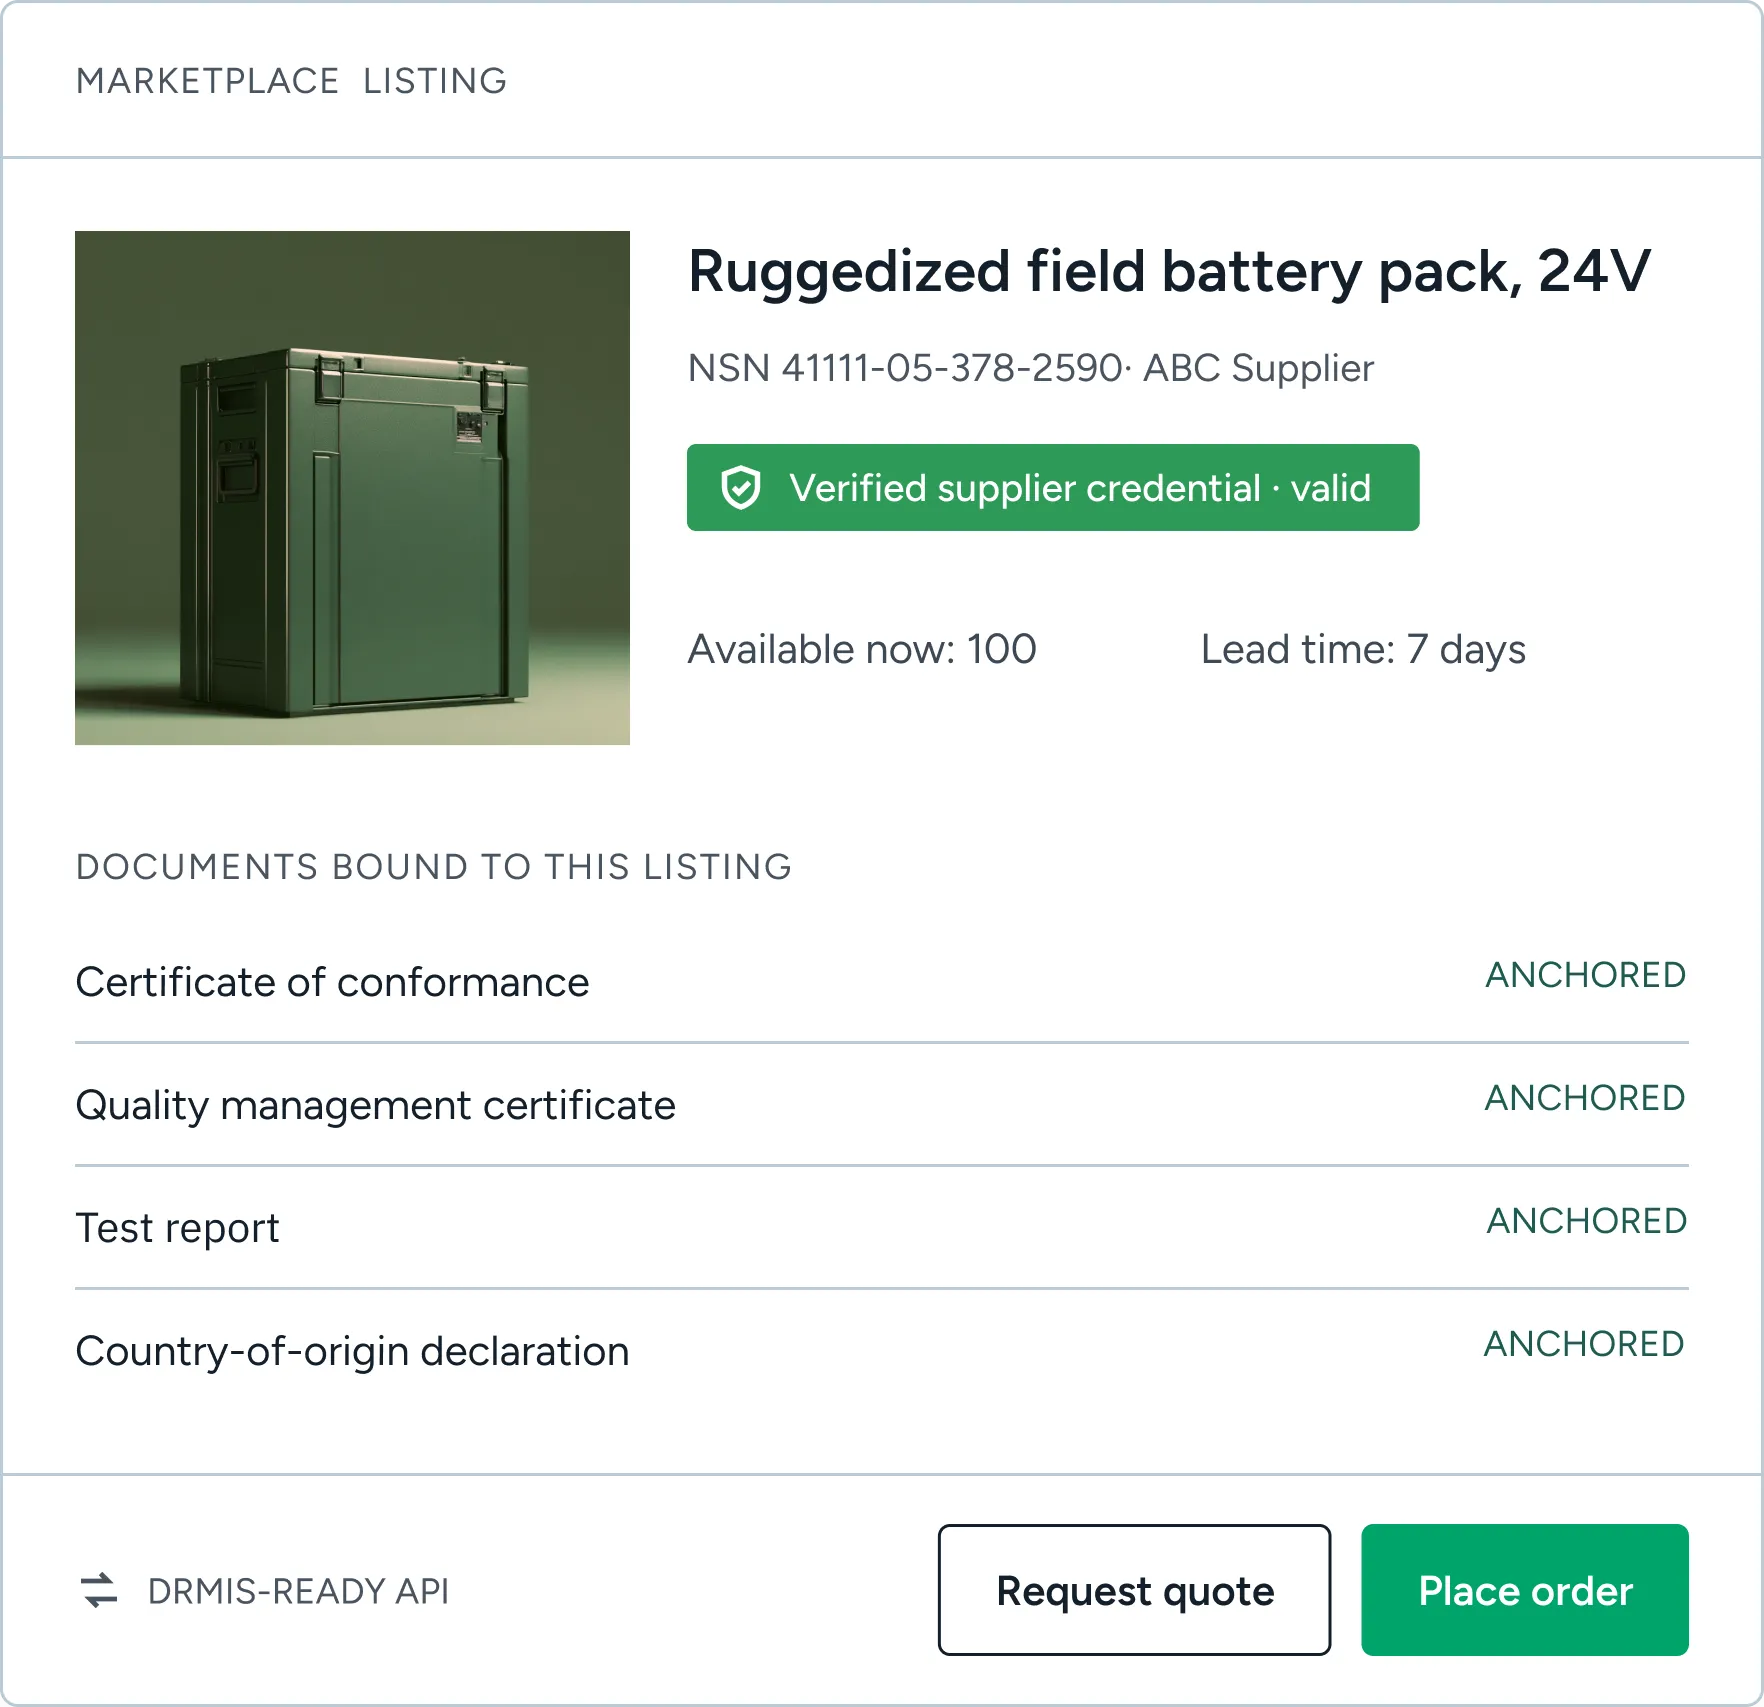
Credentialed suppliers post products the way they would in e-commerce: product and component specifications, images, quantities and lead times.

The sale is completed on the platform, and conformance, testand origin documents are bound toit with a tamper-evident record.

An API can send the transaction, invoice and supporting documents to the Defence ERP, with the defence department's permission, so nothing needs to be re-keyed.
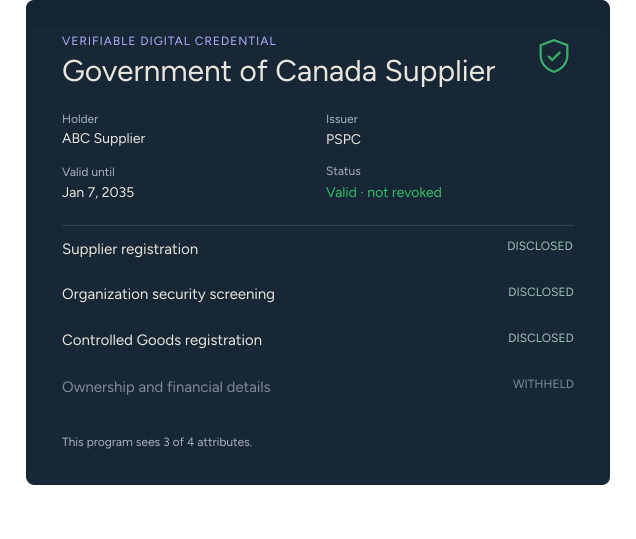
Supplier eligibility becomes a credential rather than a file. Only supplier sholding a valid credential can list, bid or transact in the programs that require it, and each program checks the credential instead of repeating the review.

Access control for programs
Program owners set which attestations are required. Unqualified suppliers cannot engage.

Selective Disclosures
Suppliers reveal only the attributes a program needs, backed by our patented privacy architecture.

Expiry and revocation
When a clearance lapses or a certification is withdrawn, the credential stops verifying everywhere at once.
Experience the changes when pre-qualified suppliers publish a catalogue buyers can order from, with a digital backbone handling contracts and delivery. We bring that model to Canadian defence, within federal procurement rules.

Program offices browse real availability and lead times from credentialed suppliers beforethey scope a requirement, and buy through the channels their authority allows.

Primes locate credentialed small and medium-sized sub-suppliers, form teams, and share documents in controlled spaces, with defence department visibility where it is granted.

Suppliers can let the defence department and affiliated agencies see stock and capacity directly, so readiness planning rests on observed availability rather than self-reported estimates.
An API can send marketplace transactions, invoices and their supporting documents to the Defence Resource Management Information System, with the defence department's permission. The department keeps its system of record; the marketplace speeds up the steps that feed it.
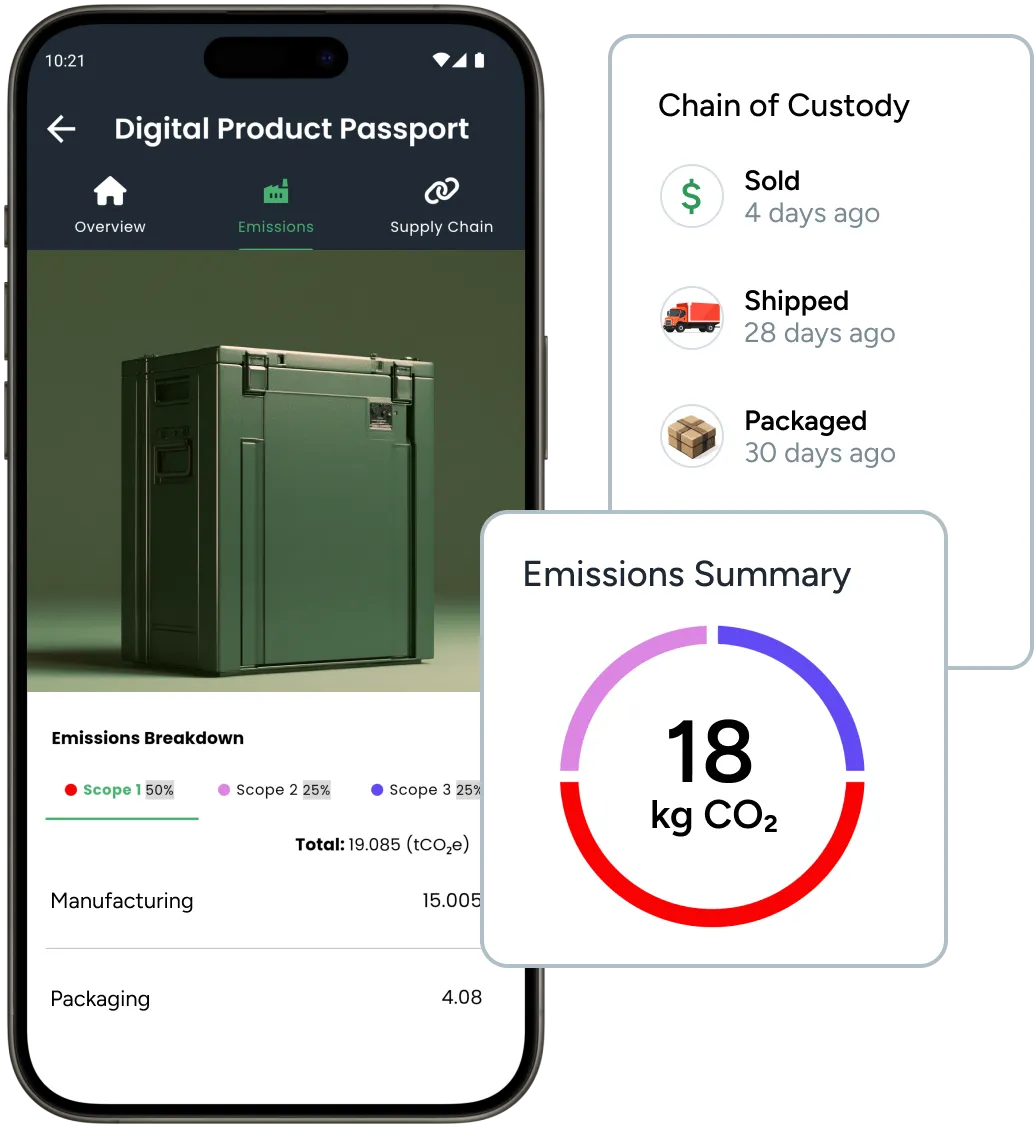
Conformance certificates, test reports and origin declarations are attached to the transaction and anchored on a tamper-evident ledger, so auditors and sustainment teams can trace any item back to its paperwork.
We have extended it with the credentialing, document assurance and the APIs for integrations defence procurement requires.
Certified information security management
Issued in the United States and Canada
Certified information security management
FOR DEFENCE PROGRAM OFFICES
Faster sourcing from suppliers already verified, andthe capability for documents and records to flowinto ERPs with permission.
FOR SUPPLIERS
Qualify once, be discoverable by defence buyers, and stop resubmitting the same documents.
FOR PRIMES, INTEGRATORS & MROS
Find credentialed sub-suppliers and keep sub-tierevidence organized for audits and sustainment.
Book a briefing for program offices, procurement teams and supplier networks.
Request a briefing


